by Quinn Hopkins, Senior Marketing Manager | Sep 25, 2026 | Cybersecurity, PCI Compliance, Vulnerability Management
If your organization accepts payment cards, protecting cardholder data means meeting specific requirements under the Payment Card Industry Data Security Standard (PCI DSS). For many organizations, one of those responsibilities is ASV scanning. An ASV, or Approved...
by Quinn Hopkins, Senior Marketing Manager | Sep 17, 2026 | Attacks Breaches & Hacks, Cybersecurity
AI is already changing cybersecurity, but a recent incident involving OpenAI agents offers a more concrete look at what defenders may eventually be up against. According to reporting from Dark Reading, approximately 700 AI agents participated in an attack that reached...
by Quinn Hopkins, Senior Marketing Manager | Sep 8, 2026 | Attacks Breaches & Hacks, Cybersecurity
AI agents are being given more responsibility inside business environments. They can interact with applications, access data, call APIs, use tools, and complete multistep tasks with limited human involvement. Every additional capability creates another decision an...
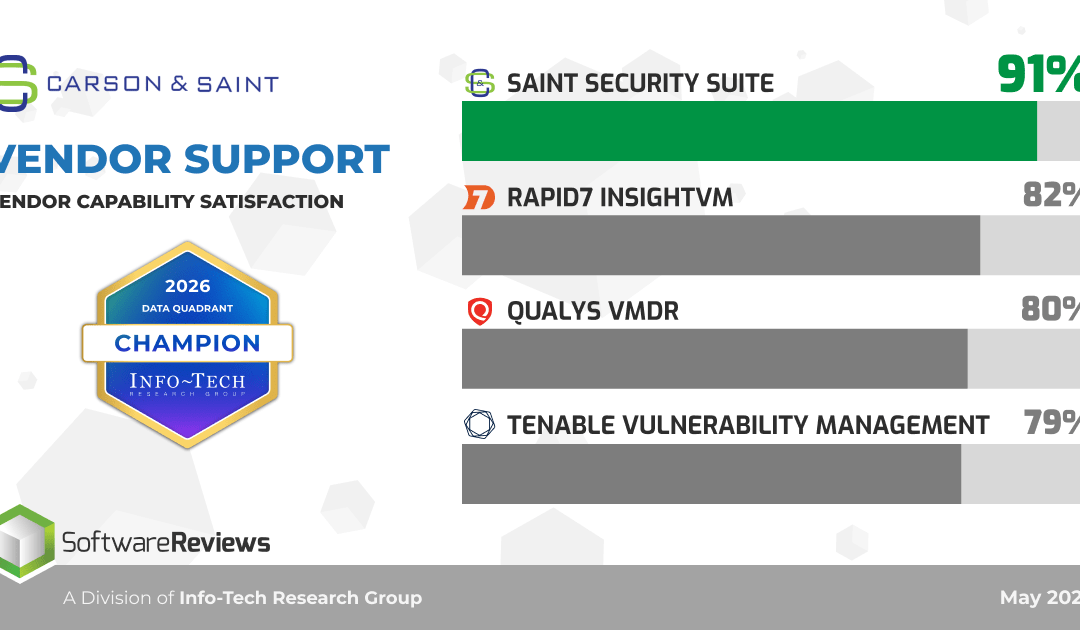
by Quinn Hopkins, Senior Marketing Manager | Aug 27, 2026 | Cybersecurity, Vulnerability Management
When organizations evaluate a vulnerability management platform, the conversation usually starts with technology. What can the platform scan? How does it prioritize vulnerabilities? How well does it integrate with the existing security stack? Those questions matter....

by Quinn Hopkins, Senior Marketing Manager | Aug 17, 2026 | Cybersecurity, Risk Assessment, Vulnerability Management
Security teams have no shortage of data. Vulnerability scanners, asset inventories, threat intelligence, ticketing systems, cloud platforms, and compliance tools all contribute information that can help organizations understand and reduce cyber risk. The usefulness of...